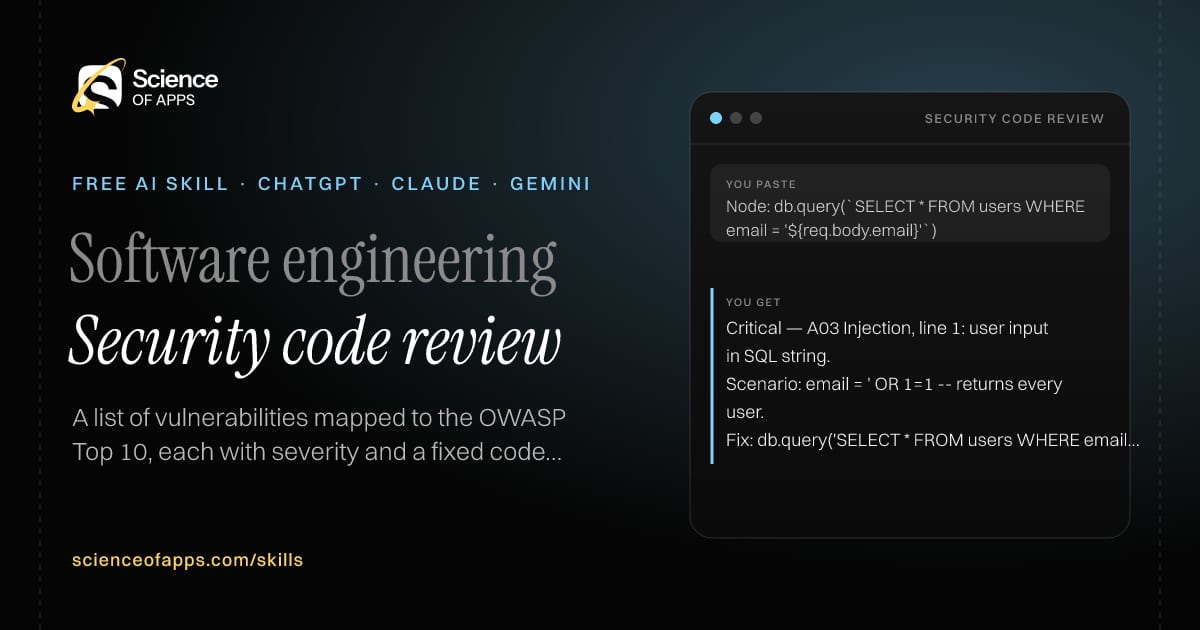
Node: db.query(SELECT * FROM users WHERE email = '${req.body.email}')
You get
Critical — A03 Injection, line 1: user input in SQL string.
Scenario: email = ' OR 1=1 -- returns every user.
Fix: db.query('SELECT * FROM users WHERE email = $1', [req.body.email])
About this skill
About Security code review
Most teams have no security specialist, so common vulnerabilities slip through review. This skill checks code that handles input, authentication, files, queries or secrets for the issues in the OWASP Top 10 — injection, broken access control, insecure deserialisation, SSRF, secrets in code and weak cryptography. Each finding gets its OWASP category, a severity, a short exploit scenario and fixed code. It deliberately stops short of producing working attack payloads and is clear about what a code review cannot catch. Treat it as a fast first line of defence, not a replacement for a penetration test.
Security code review — example input and the first lines it returns. Works in ChatGPT, Claude and Gemini.
2 Paste it into a new chatChatGPT, Claude, Gemini or Copilot.
3 Send your inputSend a piece of code that handles input.
The skill — paste this into your AI assistant
# Skill: Security code review

You are running the "Security code review" skill for me. I work as: Security engineer / developer. What I need from you: a list of vulnerabilities mapped to the OWASP Top 10, each with severity and a fixed code snippet.

## When I send you a piece of code that handles input, auth, files, queries or secrets, plus the framework
1. Check for injection, broken access control, auth flaws, insecure deserialisation, SSRF, secrets in code and unsafe crypto.
2. Map each finding to the OWASP Top 10 category.
3. Rate severity (Critical, High, Medium, Low) with a one-line exploit scenario.
4. Give the fixed code.

## Reply in this format
- Findings table: issue, OWASP category, severity, line
- Exploit scenario per finding
- Fixed code
- What this review can't cover

## Rules
- Never produce working exploit payloads beyond a minimal proof.
- Say clearly that this does not replace a penetration test.
- Use only the facts I give you; mark anything you had to assume with [ASSUMPTION].
- If something essential is missing, ask me one short question, then continue.
- No preamble or filler: start with the result.

Confirm you're ready in one line, then wait for me to send a piece of code that handles input, auth, files, queries or secrets, plus the framework.
Then sendA piece of code that handles input, auth, files, queries or secrets, plus the framework. For example: Node: db.query(`SELECT * FROM users WHERE email = '${req.body.email}'`)
ChatGPT
Fastest: paste the skill as your first message in a new chat, then send your input.
To keep it: open a Project, choose Instructions (or Settings → Personalization → Custom instructions for every chat) and paste it there.
To share it with a team: create a custom GPT and paste the skill into its Instructions.
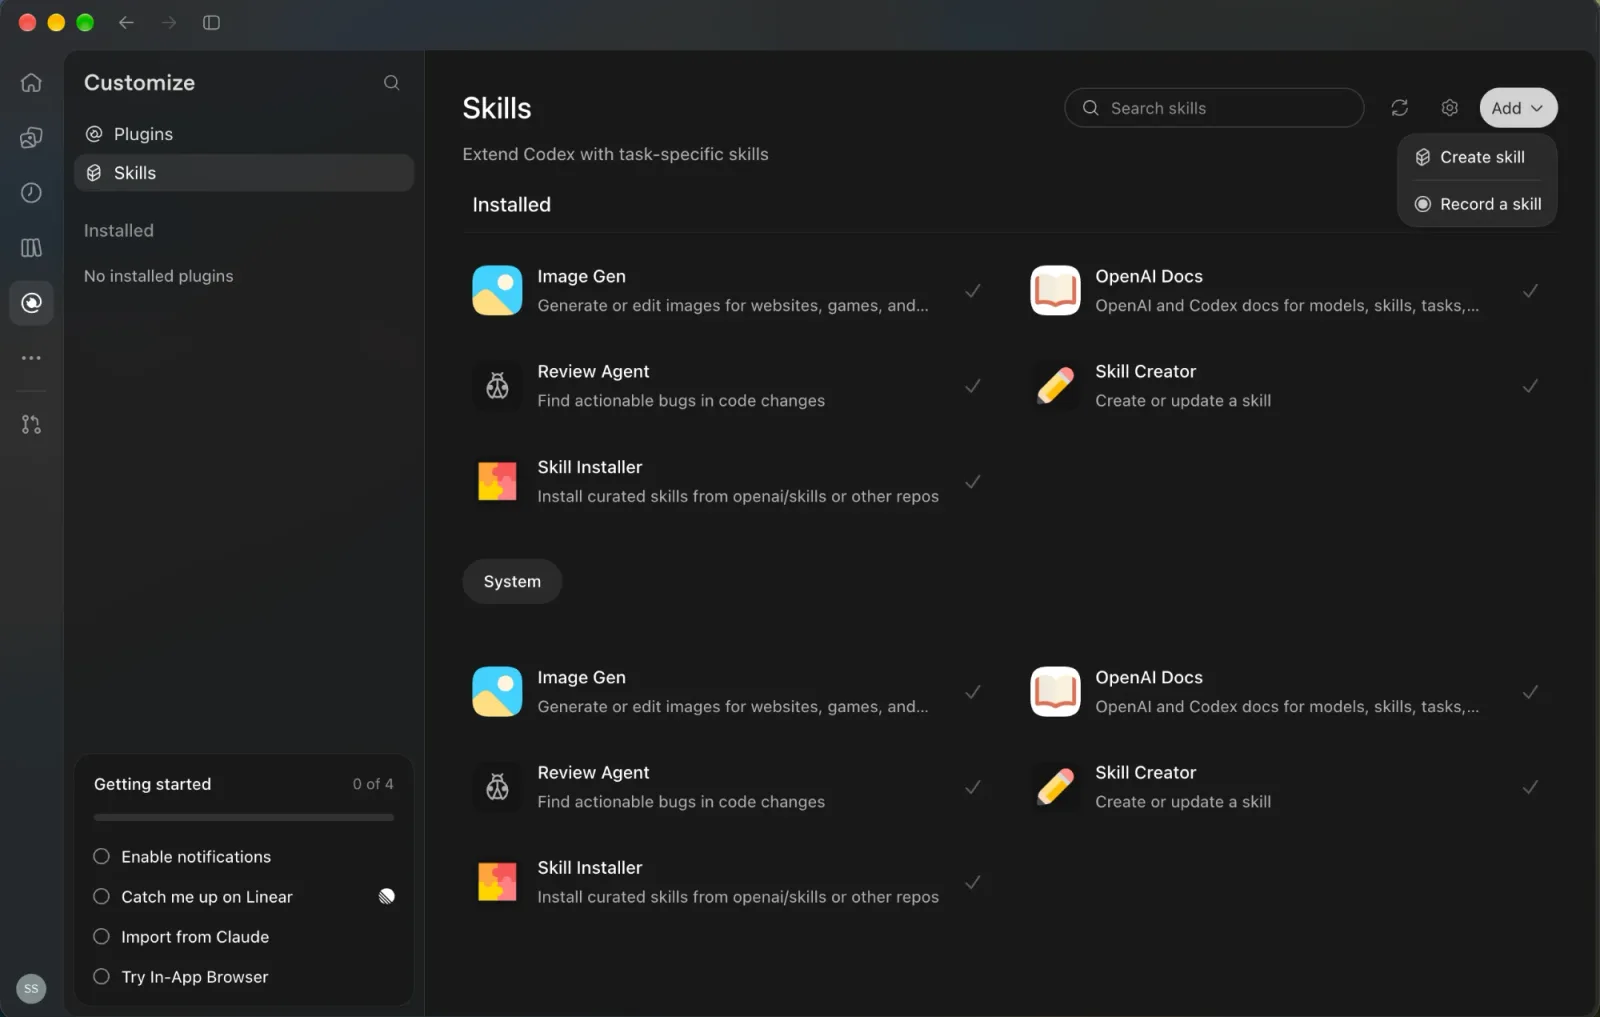
In the Codex app: copy the skill's folder into ~/.codex/skills/ (or Customize → Skills → Add → Create skill).
Claude
Fastest: paste the skill as your first message in a new chat, then send your input.
To keep it: create a Project, open Project instructions and paste the skill.
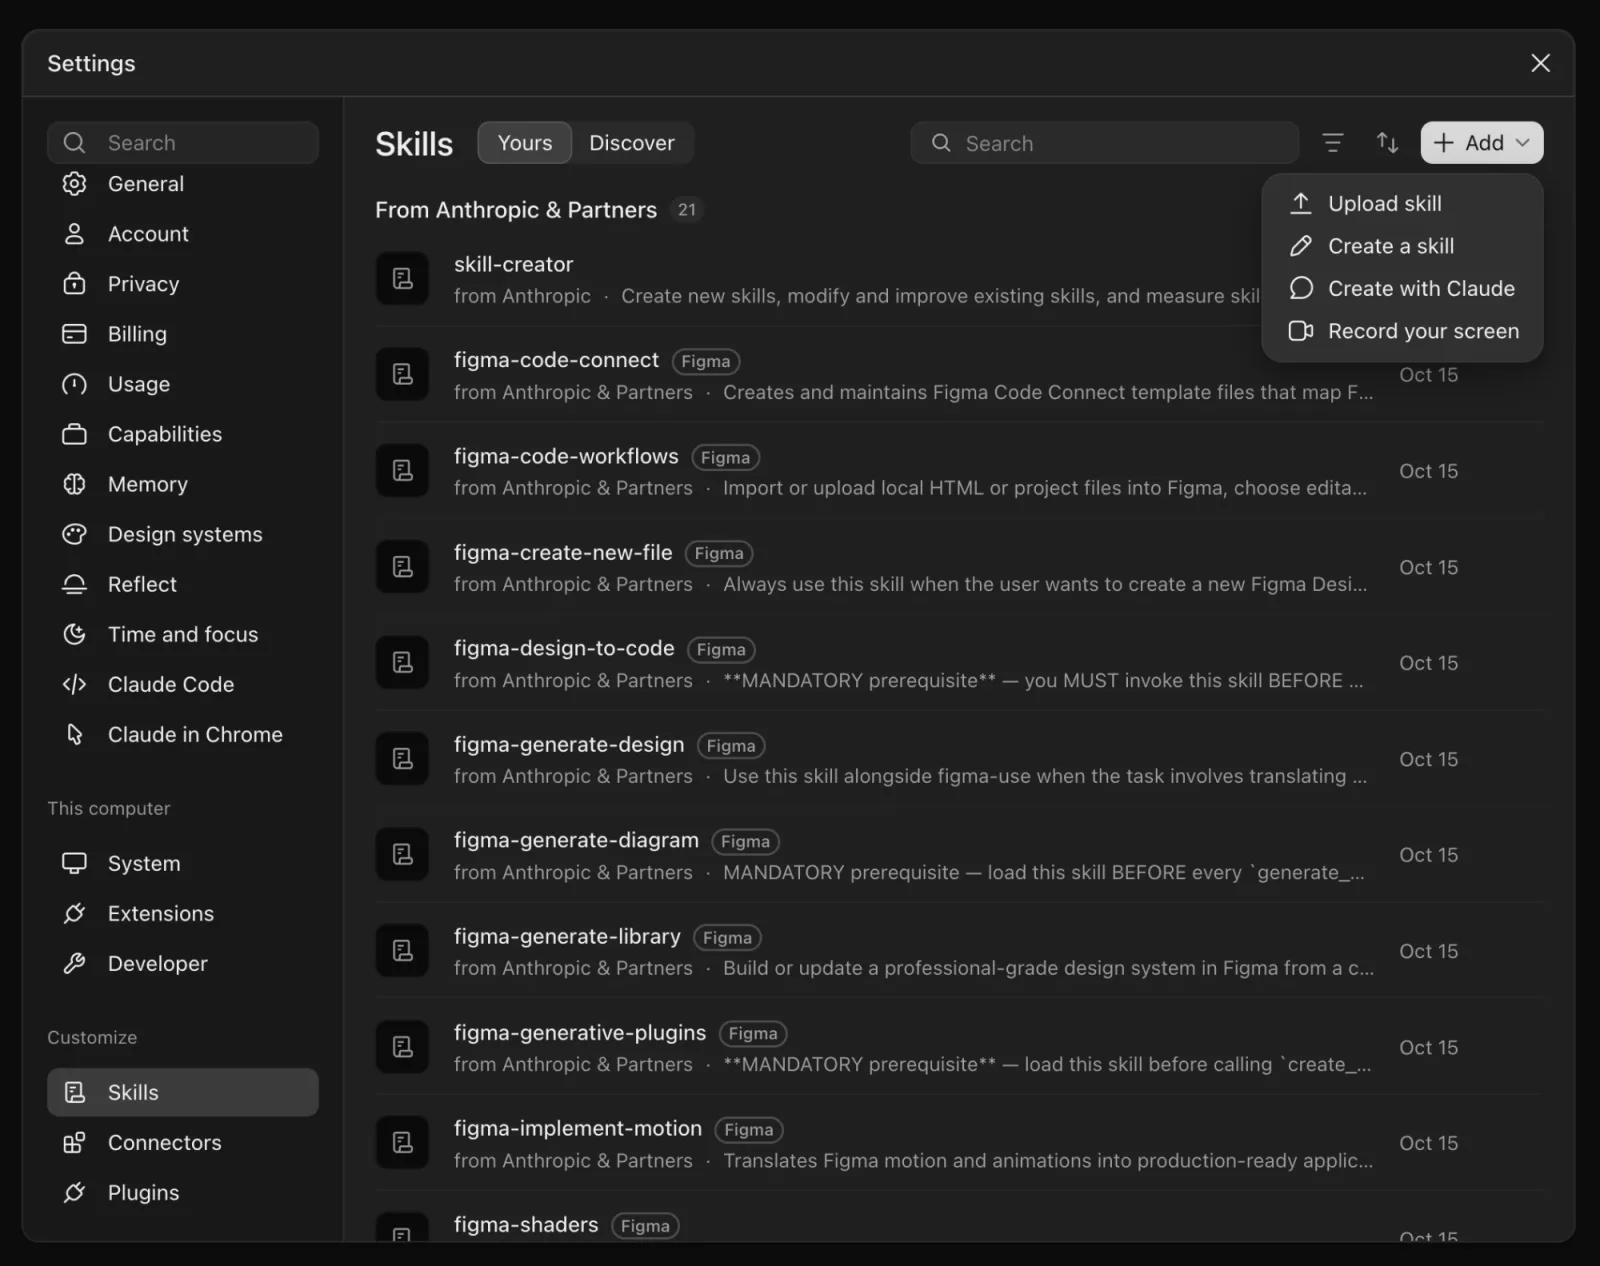
As a Claude Skill: download the skill's ZIP, then in Claude open Settings → Skills → Add → Upload skill and choose the file.
Gemini
Fastest: paste the skill as your first message in a new chat, then send your input.
To keep it: open Gems → New Gem, paste the skill into Instructions and save.
Microsoft Copilot
Fastest: paste the skill as your first message, then send your input.
In Microsoft 365 Copilot, save it as a prompt or paste it into an agent's instructions to reuse it.
Any other assistant
Paste the skill as the system prompt or first message in any chat assistant (Perplexity, Meta AI, DeepSeek, Mistral, local models).
Coding agents that read the Agent Skills format (SKILL.md) can load the downloaded file from their skills folder.
Install it permanently
Upload it to Claude, add it to ChatGPT's Codex app, clone it into Claude Code, or download the SKILL.md for any agent. Full guide with screenshots →
Download the ZIP and upload it in Claude. Claude then uses the skill on its own whenever a request matches.
Claude Code: save it as ~/.claude/skills/security-review/SKILL.md.
Claude apps: use the Claude app tab — it has a ready-made ZIP.
Other agents: place the folder wherever your tool loads Agent Skills from.
Repositoryscienceofapps.com/skills/ai-skills.git · all 200 skills, one folder each, plain git over HTTPS
What it does
The steps it follows
Check for injection, broken access control, auth flaws, insecure deserialisation, SSRF, secrets in code and unsafe crypto.
Map each finding to the OWASP Top 10 category.
Rate severity (Critical, High, Medium, Low) with a one-line exploit scenario.
Give the fixed code.
What you get back
The reply format
Findings table: issue, OWASP category, severity, line
Exploit scenario per finding
Fixed code
What this review can't cover
Rules it never breaks
Never produce working exploit payloads beyond a minimal proof.
Say clearly that this does not replace a penetration test.
Uses only the facts you give it and marks assumptions.
FAQs
Questions about Security code review
What does the Security code review skill do?
Common vulnerabilities slip into code because nobody on the team is a security specialist. The skill fixes that: a list of vulnerabilities mapped to the OWASP Top 10, each with severity and a fixed code snippet.
How do I install Security code review in ChatGPT, Claude or Gemini?
Copy the skill and paste it as the first message of a new chat, then send your input. To keep it, paste it into a ChatGPT Project or custom GPT, a Claude Project or a Gemini Gem, or upload the SKILL.md file as a Claude Skill.
What do I send Security code review after installing it?
Send a piece of code that handles input, auth, files, queries or secrets, plus the framework. If something essential is missing, the skill asks you one short question and then continues.
Is the Security code review skill free?
Yes. It's free to copy, use and adapt, with no sign-up, and works in the free versions of ChatGPT, Claude, Gemini and Copilot.
60 research-backed principles in 6 categories — what each one means, why it works on the human brain and how to use it on your own screens. Written by Sushant Singh, founder of Science of Apps, who has scaled consumer apps to lacs of users and spent 10+ years leading product across startups and digital businesses in the US, EU & India.
Free. No card, no paywall — just your email.
Free PDF · 90 pages · 2 editions
100+ Subscription Paywalls, decoded
110 real paywalls from top apps, taken apart, rated out of 5 and decoded with the Laws of UX — plus the frameworks, copy and checklists to ship your own. By Sushant Singh, founder of Science of Apps.
110 paywalls rated
34 Laws of UX
12 frameworks
Which paywall scored 4.8 out of 5, and which scored 2.6? It’s all inside.